
Related guides:
Key takeaways
- A business impact analysis (BIA) identifies which people, systems, and locations matter most when disruption hits.
- This workbook covers People, System, and Location tabs with impact-over-time scoring and RTO targets.
- Output feeds directly into your BCP/DR plan.
- SecureSlate helps connect BIA outputs to controls and audit evidence.
Overview
A BIA answers: if a critical system or team is unavailable, what breaks, how fast does impact escalate, and what do we restore first? It is a core input to business continuity planning and a common request in SOC 2 and ISO 27001 audits.
What makes it useful
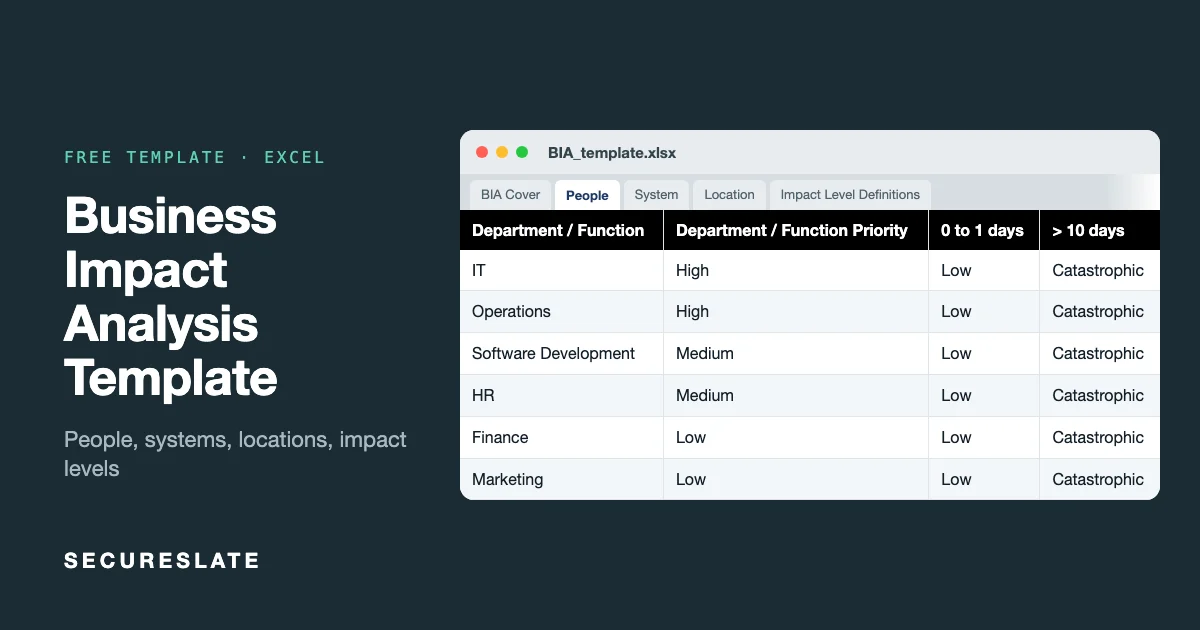
- Five structured tabs: Cover, People, System, Location, and Impact Level Definitions.
- Impact over time: Score Low through Catastrophic at 0 to 1 days, 2 to 4 days, 5 to 10 days, and 10+ days.
- RTO and MTPoD: Set recovery targets per system and location.
- Contingency column: Document the actual failover or workaround for each dependency.
Download the template
Fill document control on BIA Cover before your first workshop with operations and engineering.
Tab-by-tab walkthrough
BIA Cover
Organization name, version, date, BCMS owner, classification, and review cycle.
Impact Level Definitions
Calibrate Low, Medium, High, and Catastrophic tiers. Adjust financial thresholds and guidance to match your business.
People
List departments with priority, head of function, staffing levels, work location, impact over time, and system dependencies.
System
For each system: what it does, who uses it, RTO, MTPoD, impact over time, people dependencies, and contingency plan. Include production app, auth, database, and key SaaS tools.
Location
Offices, hosting sites, and cloud regions with the same RTO, MTPoD, and impact columns as systems.
How to use it as audit evidence
| Evidence type | Template tab |
|---|---|
| Business impact methodology | Impact Level Definitions |
| Critical functions identified | People |
| Recovery priorities | System RTO/MTPoD columns |
| Site dependencies | Location |
| Management review | BIA Cover version and date |
Review annually or after major architecture, vendor, or org changes.
Common mistakes
- One generic "IT platform" row instead of separate critical services
- RTO targets set without testing actual recovery time
- Contingency column left blank
- BIA completed once and never updated
How to run a BIA in five steps
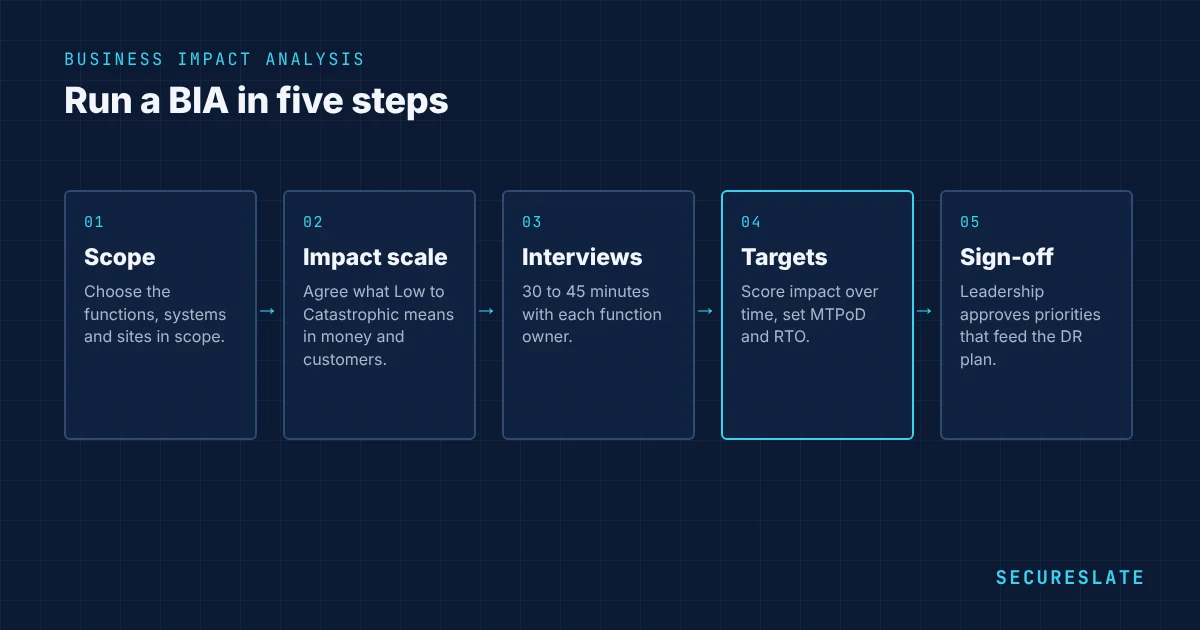
- Scope it. Decide which parts of the business are in scope. For a SaaS company of up to 50 people that usually means the product, customer support, finance and the people and tools behind them. Fill in the
BIA Covertab. - Agree the impact scale. Before any interviews, set what Low, Medium, High and Catastrophic mean in money, customers, legal exposure and reputation on the
Impact Level Definitionstab. Everyone then scores against the same scale. - Interview function owners. Spend 30 to 45 minutes with each department head. Ask what they do, which systems and people they rely on, and what happens if they stop for one day, four days, ten days and longer.
- Score and set targets. For each function (on the
Peopletab), system and location, record impact over time and choose the RTO and MTPoD. The MTPoD (maximum tolerable period of disruption, also written MTPD) is the point where impact becomes unacceptable. The RTO must be shorter, so you can recover before that point. - Review and sign off. Walk leadership through the results, agree the recovery priorities, and record the approval and date. These priorities then feed your BCP and disaster recovery plan.
Questions to ask in BIA interviews
Use the same questions with every function so the answers can be compared:
- What are the three most important things your team delivers each week?
- Which systems, vendors and people do you need to deliver them?
- If those were unavailable for one day, who would notice and what would it cost?
- At what point would we break a contract, miss a regulatory deadline or lose customers?
- What workaround could you use, and for how long would it hold?
- Are there busy periods, such as month end or a product launch, when an outage would hurt more?
- Who is the one person you could not work without, and who backs them up?
Write the answers into the People and System tabs straight after each interview, while the detail is fresh.
Worked example
Here is how one row might look for a small B2B SaaS company:
| Field | Example |
|---|---|
| System | Production application (customer-facing) |
| Used by | All customers, support team |
| Impact in the first 24 hours | High: customers cannot log in, SLA credits start after 4 hours |
| Impact after 24 hours | Catastrophic: enterprise customers can terminate, renewals at risk |
| MTPoD | 24 hours |
| RTO | 4 hours |
| Depends on | Cloud hosting, identity provider, database, DNS |
| Contingency | Restore from backup into a second region; status page updates every 30 minutes |
The example shows why the contingency column matters. An RTO of 4 hours means nothing unless someone has written down, and tested, how the service is restored in that time.
How the BIA connects to your compliance program
A BIA is the evidence that your continuity and recovery decisions are based on business need rather than guesswork.
- ISO 27001 expects information security to continue during disruption (Annex A 5.29) and ICT readiness for business continuity (Annex A 5.30). A BIA is the usual way to show how you set those requirements.
- ISO 22301 makes the BIA a core requirement of a business continuity management system.
- SOC 2 Availability criteria expect recovery objectives and plans. Auditors often ask how RTOs were chosen, and the BIA is the answer.
- Customer questionnaires regularly ask whether you have a BIA and when it was last reviewed.
How SecureSlate helps
SecureSlate connects BIA outputs to continuity controls, evidence refresh, and audit-ready exports.
FAQ
How is a BIA different from a BCP/DR plan?
The BIA identifies impact and priorities. The BCP/DR plan documents how you recover. Use both templates together.
Who should run the BIA workshop?
Typically security or operations, with system owners from engineering and business units.
Is a BIA required for SOC 2?
Not always as a named document, but it commonly supports availability and continuity expectations.
How long does a BIA take?
For a company of up to 50 people, plan for about two weeks: a few days to prepare the impact scale, one interview per function, and a review meeting. The first one takes longest. Annual updates are much quicker.
What is the difference between RTO and MTPoD?
The MTPoD is the longest a function can be disrupted before the harm becomes unacceptable. The RTO is your target for restoring it, and it must be shorter than the MTPoD.
How often should a BIA be updated?
At least once a year, and after any major change such as a new product, a new critical vendor, a move to a new cloud region or a reorganization.
Disclaimer (legal note)
This article is for general information only and is not legal, regulatory, or professional advice. Requirements vary by framework, industry, and jurisdiction. Consult qualified advisors for your specific obligations.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds
