
Related guides:
- 10 cybersecurity kpis that are revolutionizing the way cisos protect their companies
- risk assessment template
- soc 2 readiness checklist template
Key takeaways
- Security metrics prove your program is operating, not just documented on paper.
- This workbook tracks 10 KPIs across 12 months with RAG (Red/Amber/Green) status and dedicated detail tabs.
- Includes MFA coverage, patch SLA, vulnerability aging, MTTD, MTTR, and evidence freshness.
- SecureSlate automates metric collection and evidence refresh alerts.
Overview
Boards and auditors increasingly ask for numbers: MFA adoption, patch compliance, open critical vulns, and whether evidence is current. A monthly KPI tracker gives security leaders a single view without building dashboards from scratch.
What makes it useful
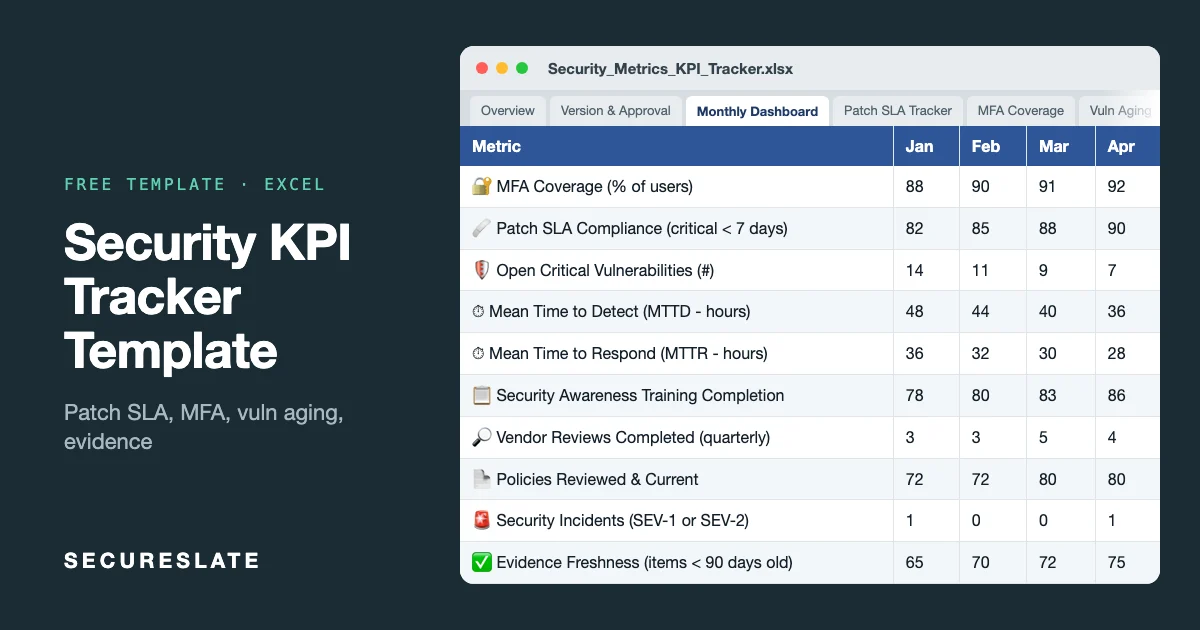
- Monthly dashboard: 12-month view of 10 core security KPIs with targets and RAG status.
- Patch SLA tracker: Per-CVE rows with severity, SLA deadline, patched date, and SLA Met flag.
- MFA coverage: Per-system user counts with auto-calculated coverage percentage.
- Vuln aging: Days open with SLA breach flags for overdue findings.
- Evidence freshness: Days until due with Overdue alerts for audit evidence.
Download the template
Update the dashboard on the first business day of each month. Present to leadership quarterly.
Tab-by-tab walkthrough
Overview and Version & Approval
Document owner and review cadence. Set annual KPI targets on the dashboard before January.
Monthly Dashboard
Ten metrics across Jan to Dec: MFA Coverage %, Patch SLA Compliance %, Open Critical Vulns, MTTD (hours), MTTR (hours), Training Completion %, Vendor Reviews Completed, Access Reviews On Time %, Evidence Freshness %, and Incident Count. RAG thresholds are pre-set; adjust targets to your program.
Patch SLA Tracker
Log each CVE: system, severity, CVSS, discovered date, SLA deadline, patched date, and SLA Met (Yes/No). Critical patches typically target 7 days.
MFA Coverage
Per application: total users, MFA enabled, MFA disabled, coverage %, and target (usually 100%). Flag exceptions with notes.
Vuln Aging
Open findings with days open and SLA Breach flag. Link remediation plans to tickets.
Evidence Freshness
Per control evidence item: owner, last updated, next due, days until due, and status (Current or Overdue). Prevents audit surprises from stale screenshots.
How to use it as audit evidence
| Metric | Why auditors care | Template tab |
|---|---|---|
| MFA coverage | Access control effectiveness | MFA Coverage |
| Patch SLA | Vulnerability management | Patch SLA Tracker |
| Vuln aging | Risk remediation speed | Vuln Aging |
| Evidence freshness | Continuous control operation | Evidence Freshness |
Export monthly snapshots for your audit evidence folder.
Common mistakes
- Metrics collected once for the audit, then abandoned
- Targets set without baseline data from the first month
- MFA coverage counted without excluding service accounts properly
- Evidence freshness tracker not linked to actual evidence locations
How to choose the right security KPIs
A good security KPI meets four tests:
- It is tied to a risk. MFA coverage maps to account takeover. Patch SLA maps to exploitation of known vulnerabilities. If you cannot name the risk, drop the metric.
- It is measurable from a system, not a guess. Pull it from your identity provider, scanner or ticketing tool so it can be repeated each month.
- Someone owns it. Every KPI needs a named owner who explains a red status and fixes it.
- It drives a decision. If a metric turning red would not change anything, it is noise.
Start with the ten metrics in the template, then remove any that fail these tests for your company and add one or two that reflect your biggest risks.
Suggested targets and RAG thresholds
Use these as starting points for a SaaS company of up to 50 people, then adjust after your first three months of real data.
| KPI | Green | Amber | Red |
|---|---|---|---|
| MFA coverage (human accounts) | 100% | 95 to 99% | Below 95% |
| Critical patches within SLA (7 days) | 95% or more | 85 to 94% | Below 85% |
| Open critical vulnerabilities | 0 | 1 to 2 | 3 or more |
| Mean time to detect (MTTD) | Under 24 hours | 24 to 72 hours | Over 72 hours |
| Mean time to respond (MTTR) | Under 8 hours | 8 to 24 hours | Over 24 hours |
| Security training completion | 100% | 90 to 99% | Below 90% |
| Access reviews completed on time | 100% | 90 to 99% | Below 90% |
| Evidence freshness | 95% or more current | 85 to 94% | Below 85% |
Set targets you can defend. A target nobody meets for six months turns the whole dashboard red and people stop reading it.
Building a monthly reporting routine
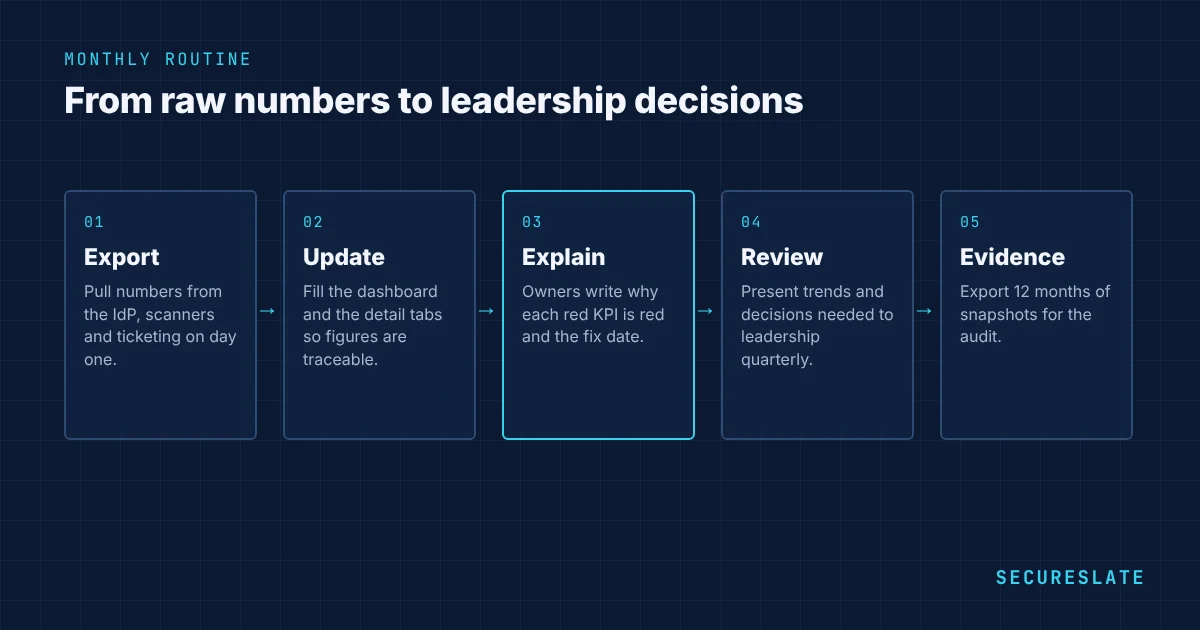
- First business day: export the numbers from each source system and fill in the
Monthly Dashboard. - Same day: update the detail tabs (patches, MFA, vulnerability aging, evidence) so the dashboard numbers can be traced.
- Within the first week: the security owner writes three lines for each red metric: why it is red, what is being done, and by when.
- Quarterly: present the dashboard and the trend to leadership or the board, with decisions you need from them.
- Before an audit: export the last 12 months as evidence that controls operated throughout the period.
The routine matters more than the tool. A spreadsheet updated every month is stronger evidence than a dashboard nobody checks.
Presenting metrics to leadership
Executives and boards rarely want ten numbers. Lead with three things: the overall trend (improving, stable or worse), the one or two risks that need a decision or budget, and how you compare with what customers and auditors expect. Keep the full table as an appendix. Show trends over at least three months, because a single month can be misleading.
How SecureSlate helps
SecureSlate automates security metrics, evidence collection, and freshness alerts so your KPI dashboard reflects live program health.
FAQ
How many KPIs should a SaaS startup track?
Start with 5 to 10. This template includes the most common set auditors and boards ask about.
How often should we update metrics?
Monthly for operational KPIs. Evidence freshness should be checked weekly during audit periods.
Can this replace a SIEM dashboard?
No. It complements automated tooling with a leadership-friendly summary and audit trail.
What are examples of cybersecurity KPIs?
Examples of cybersecurity KPIs include mean time to detect and respond, patch compliance rate, phishing failure rate, and percentage of access reviews completed. Good KPIs tie to risk, not just activity.
- Detection/response: MTTD and MTTR.
- Hygiene: percentage of systems patched within SLA.
- People: phishing simulation failure rate.
What is the difference between a security metric and a KPI?
A metric is any measurement, such as the number of phishing emails blocked. A KPI is a metric you have chosen to track against a target because it shows whether the security program is achieving its goals.
Which KPIs do SOC 2 and ISO 27001 auditors look at?
Auditors test controls rather than KPIs, but the same numbers support their samples: MFA coverage, patch timelines, vulnerability remediation, access review completion, training completion and incident response times.
Should service accounts count toward MFA coverage?
Track them separately. Service accounts often cannot use MFA, so protect them with other controls such as key rotation, IP restrictions and least privilege, and document the exception.
Disclaimer (legal note)
This article is for general information only and is not legal, regulatory, or professional advice. Requirements vary by framework, industry, and jurisdiction. Consult qualified advisors for your specific obligations.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds