
Related guides:
Key takeaways
- A BCP/DR plan documents how your SaaS service recovers from outages with clear RTO, RPO, and MTPD targets.
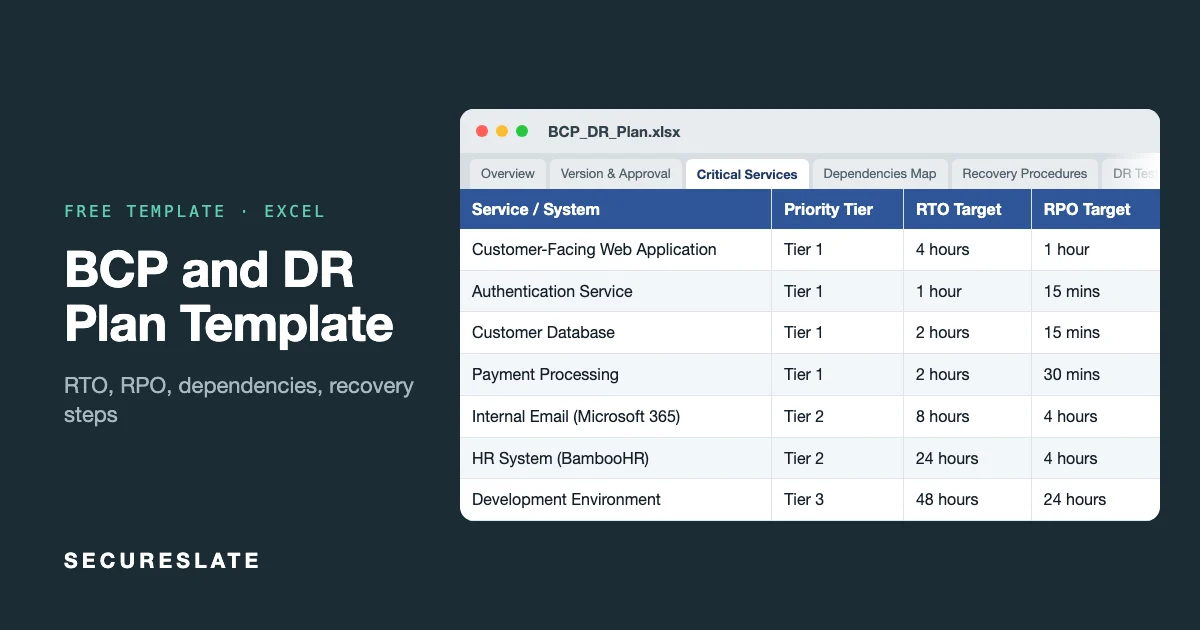
- This workbook includes a critical services register, dependency map, recovery procedures, and DR test log.
- Aligns with ISO 22301 practices and SOC 2 Availability criteria.
- SecureSlate helps connect continuity controls to evidence and test records.
Overview
SaaS customers expect uptime commitments. A DR plan proves you know which services matter most, what depends on what, and how you would restore production if a region or vendor fails.
What makes it useful
- Tiered services: Tier 1/2/3 priority with RTO, RPO, and MTPD per service.
- Dependency register: Flags single points of failure (identity provider, payment gateway, DNS).
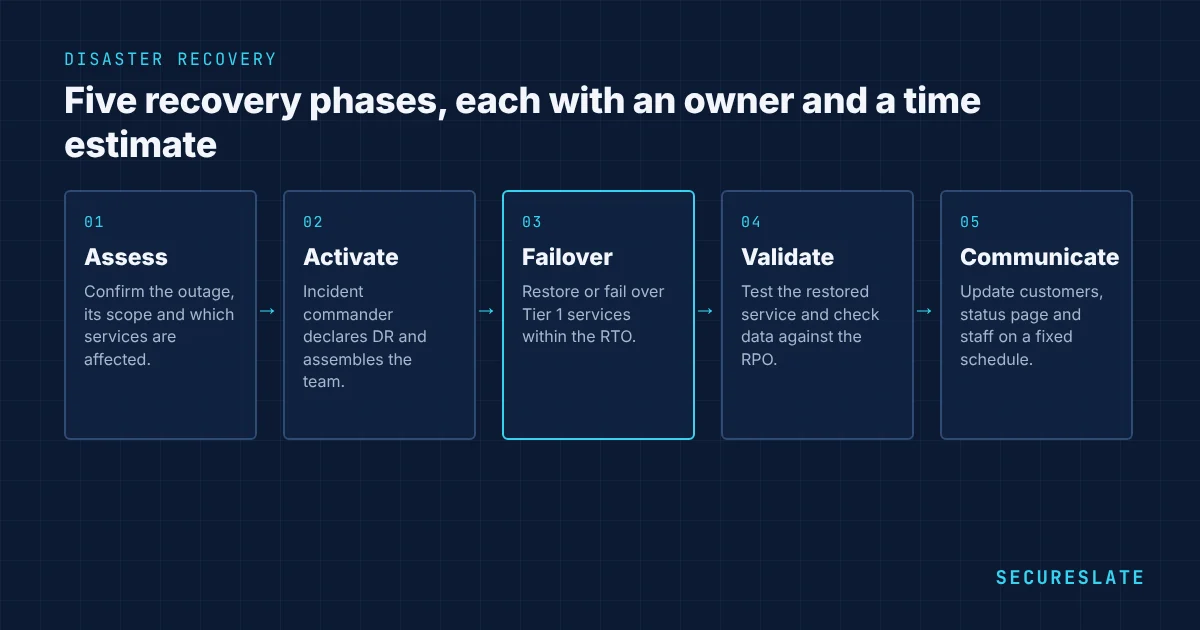
- Step-by-step recovery: Phased procedures (Assess, Activate, Failover, Validate) with owners and time estimates.
- Test results log: Records actual vs target RTO/RPO with pass/fail outcomes.
Download the template
Pair this with the BIA template to align business impact with technical recovery targets.
Tab-by-tab walkthrough
Overview and Version & Approval
Document owner, scope, and annual review sign-off.
Critical Services
Register each service with Business Function, Priority Tier, RTO Target, RPO Target, MTPD, Service Owner, Recovery Team, and Backup Location. Start with customer-facing app, auth, database, and payment processing.
Dependencies Map
List dependencies per service: type (cloud, identity, payment, DNS), provider, criticality, single-point-of-failure flag, and mitigation. Address every "Yes" in the SPOF column.
Recovery Procedures
Phased steps per service: Assess, Activate, Failover, Validate, and Communicate. Include estimated time and named owner per phase.
DR Test Results
Log each tabletop, partial failover, or full simulation. Record target vs actual RTO/RPO and lessons learned. Failed tests are valuable evidence if follow-up actions are tracked.
How to use it as audit evidence
| Control area | Template tab |
|---|---|
| Recovery objectives | Critical Services RTO/RPO/MTPD |
| Dependency awareness | Dependencies Map |
| Documented procedures | Recovery Procedures |
| Plan tested annually | DR Test Results |
SOC 2 Availability auditors commonly sample DR test results from the last 12 months.
Common mistakes
- RTO targets that do not match actual failover capability
- Dependencies missing third-party SaaS tools
- Recovery steps never tested end to end
- Plan not updated after cloud region or architecture changes
BCP vs disaster recovery plan
A business continuity plan covers how the business keeps serving customers during any disruption, including people, offices, suppliers and communication. A disaster recovery plan covers how you restore the technology itself. For a side-by-side comparison, see business continuity vs disaster recovery.
For most SaaS companies under 50 people, the product is the business, so the DR plan carries most of the weight. Keep both in one workbook, as this template does, so the business priorities and the technical recovery steps never drift apart.
How to set RTO, RPO and MTPD targets
Recovery targets should come from the business, then be tested against what engineering can actually deliver.
- MTPD (maximum tolerable period of disruption, also written MTPoD) is the point where an outage causes unacceptable harm: SLA credits you cannot absorb, churn, or regulatory exposure. Take it from your BIA.
- RTO (recovery time objective) is how fast you commit to restore the service. It must be shorter than the MTPD, with a margin for decision time.
- RPO (recovery point objective) is how much data you can afford to lose, measured in time. It is set by your backup or replication frequency, not by a policy statement.
A practical way to set them:
- List every customer-facing service and the internal services it depends on.
- Ask the business owner what happens after 1 hour, 4 hours, 24 hours and 72 hours of downtime.
- Set the MTPD at the first point where the answer becomes unacceptable.
- Set the RTO at half the MTPD or less, so there is time to detect, decide and recover.
- Check the RPO against real backup settings. If backups run nightly, your RPO is 24 hours, whatever the plan says.
- Run a test. If the measured recovery time is longer than the RTO, fix the architecture or change the target.
Running your first DR test
A first test does not need to be a full failover. Start small and build up.
- Tabletop exercise (60 to 90 minutes). Walk through a scenario such as "our primary cloud region is down" with engineering, support and leadership. Read the recovery procedure aloud and note every step where someone is unsure who acts or what to do.
- Backup restore test. Restore last night's database backup into an isolated environment and time it. Confirm the data is complete and the application can read it. This one test proves your RPO and a large part of your RTO.
- Partial failover. Fail one non-critical service over to its secondary location during a planned window.
- Full simulation. Once the first three pass, schedule a full failover of a Tier 1 service, ideally once a year.
Record each test in the DR Test Results tab with the target and actual times. Auditors care less about a perfect result than about a test that happened, a record of what went wrong, and tracked actions to fix it.
Roles and responsibilities
Name a person, not a team, for each role, and a backup for each person.
- Incident commander: declares the disaster, makes the failover decision and owns the timeline.
- Technical recovery lead: runs the recovery procedure for each affected service.
- Communications lead: updates customers, the status page and internal staff on a fixed schedule.
- Business owner: confirms when the restored service is good enough to call the incident resolved.
Store the contact list outside your production systems. If your identity provider is down, people still need to reach each other.
Keeping the plan current
Review the plan at least once a year and after any of these changes: a new cloud region or provider, a new critical vendor, a major architecture change, a change in SLA commitments, or a real incident. Record each review in the Version & Approval tab so you can show the plan is maintained, not written once for an audit.
How SecureSlate helps
SecureSlate tracks continuity controls, evidence freshness, and DR test records so your BCP program stays audit-ready.
FAQ
How is BCP different from a BIA?
The BIA identifies business impact and priorities. The BCP/DR plan documents how you recover services to meet those priorities.
How often should we test DR?
At minimum one tabletop per year. Many SaaS teams run one partial failover test annually.
What RTO should a SaaS app target?
Depends on your SLA. Tier 1 production services often target 1 to 4 hours RTO with 15 to 60 minute RPO.
What is the difference between RTO and RPO?
RTO is how long you can take to restore a service. RPO is how much data, measured in time, you can afford to lose. A 4-hour RTO with a 15-minute RPO means the service is back within 4 hours and loses no more than the last 15 minutes of data.
Do small companies really need a DR plan?
Yes, if customers depend on your service. SOC 2 Availability, ISO 27001 (Annex A 5.29 and 5.30) and many customer security questionnaires ask for one. A short, tested plan is better than a long, untested one.
Where should the DR plan be stored?
Somewhere you can reach when production is down: a copy outside your main cloud account and identity provider, plus a printed or offline copy for the incident commander.
Disclaimer (legal note)
This article is for general information only and is not legal, regulatory, or professional advice. Requirements vary by framework, industry, and jurisdiction. Consult qualified advisors for your specific obligations.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds