
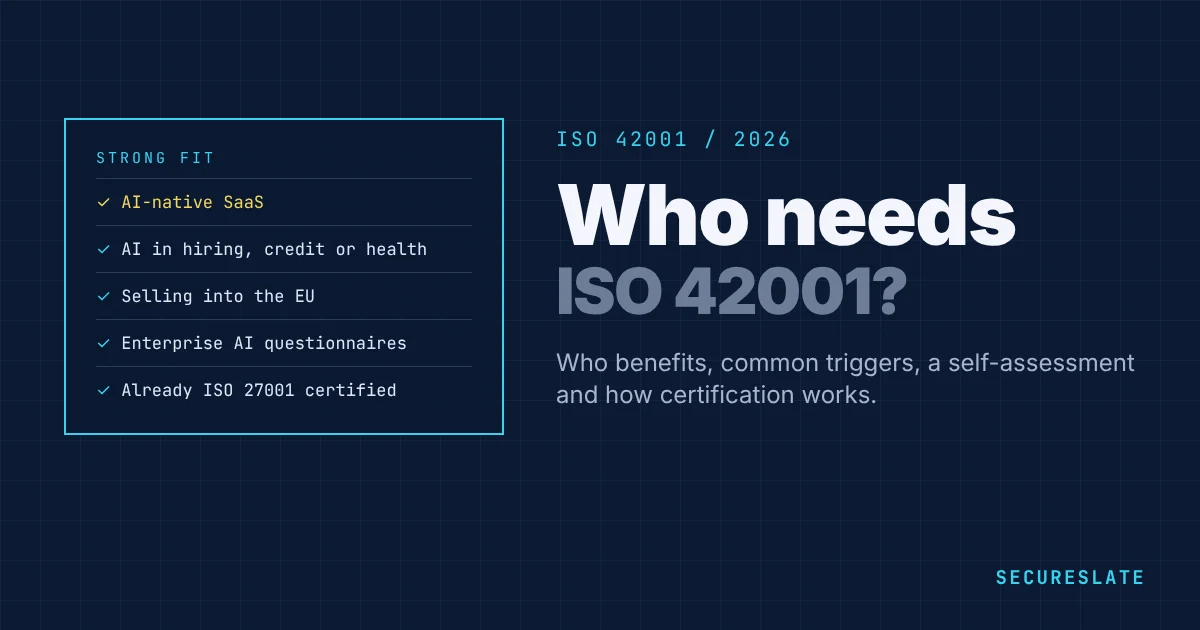
ISO/IEC 42001 certifies an Artificial Intelligence Management System (AIMS), a structured approach to governing AI across the lifecycle. It is most valuable when AI is core to your product or when buyers and regulators expect demonstrable AI governance.
Related: What is ISO 42001? · Collection
Key takeaways
- Strong fit: AI-native SaaS, enterprises shipping ML features, and vendors in regulated sectors.
- Often pursued after ISO 27001 or SOC 2, reusing security and risk evidence.
- Certification signals operational AI governance, not only principles on a website.
- EU-facing companies frequently pair 42001 with EU AI Act planning.
Who typically pursues ISO 42001
| Profile | Why |
|---|---|
| AI product companies | Customer diligence on models, data, monitoring |
| Enterprises using AI at scale | Internal governance and supplier assurance |
| Regulated industries | Healthcare, finance, public sector AI programs |
| Vendors to enterprises | RFPs requesting AI management standards |
Common triggers
- Enterprise security questionnaires ask for AI governance evidence
- Board or risk committee mandates an AI policy with audit trail
- Launching high-risk AI features (automation, agents, biometric-adjacent use)
- Expanding into EU markets with AI Act timelines
Does ISO 42001 apply to you? A quick self-assessment
ISO 42001 can be used by any organization that develops, provides or uses AI systems. Answer these questions:
- Is AI part of a product or service you sell?
- Do customers ask about AI governance, model risk or responsible AI in security reviews or RFPs?
- Do you make decisions about people (hiring, credit, access to services, healthcare) with the help of AI?
- Do you operate in, or sell into, the European Union?
- Do you already hold ISO 27001 or SOC 2 and want to extend your program?
- Is your board or investors asking how AI risk is managed?
If you answered yes to three or more, ISO 42001 is likely worth planning for. If only one or two apply, start with an AI policy, an AI system inventory and a risk register, and review again in six months.
Builders, providers and users of AI
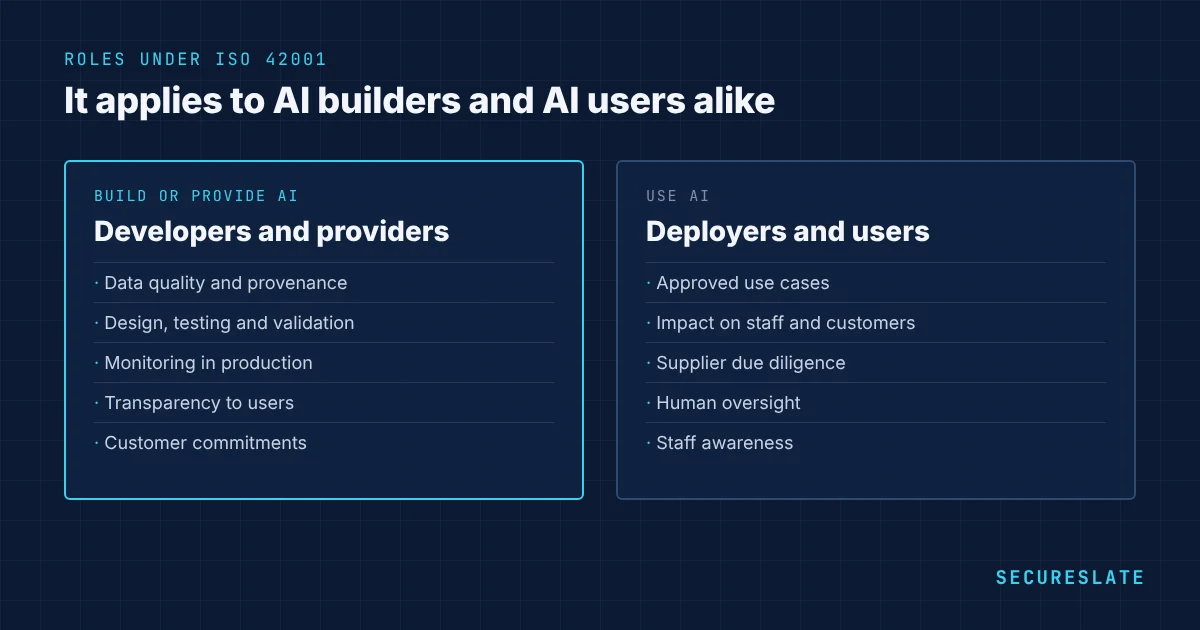
ISO 42001 is not only for companies that train their own models.
- AI developers build or train models and systems, and carry the heaviest lifecycle obligations: data, design, testing and monitoring.
- AI providers offer AI products or services to others, often built on third-party models. They focus on intended use, transparency, supplier management and customer commitments.
- AI users deploy AI tools inside their own business. They focus on approved use, impact on employees and customers, and supplier due diligence.
Many SaaS companies are all three: they build features, sell them to customers and use AI tools internally.
How certification works
- Build the AI management system: scope, AI policy, roles, inventory, risk and impact assessments, Statement of Applicability, controls and internal audit.
- Stage 1 audit: an accredited certification body reviews your documentation and readiness.
- Stage 2 audit: the auditor tests whether the management system and controls operate as described.
- Certificate: valid for three years, with surveillance audits in years two and three and a recertification audit at the end of the cycle.
Organizations that already hold ISO 27001 can often run combined audits, which reduces audit days and disruption.
Industries where ISO 42001 matters most
- Healthcare and life sciences: AI that supports diagnosis, triage, scheduling or clinical documentation affects patient safety and privacy. Buyers expect evidence of testing, human oversight and data governance.
- Financial services: credit decisions, fraud detection and customer service bots face scrutiny on fairness, explainability and model risk management.
- HR and recruiting technology: AI used to screen or rank candidates is closely watched by regulators, and is classed as high-risk under the EU AI Act.
- Public sector suppliers: government buyers increasingly ask for structured AI governance in procurement.
- B2B SaaS with AI features: enterprise customers add AI questions to security reviews, and a certificate answers many of them at once.
ISO 42001 compared with other AI frameworks
| ISO 42001 | NIST AI RMF | EU AI Act | |
|---|---|---|---|
| Type | International management system standard | Voluntary framework | Law |
| Certifiable | Yes, by accredited certification bodies | No | Conformity assessment for certain high-risk systems |
| Scope | Any organization that develops, provides or uses AI | Any organization managing AI risk | AI systems placed on the EU market or affecting people in the EU |
| Best used for | Proving AI governance to customers and partners | Structuring internal AI risk management | Meeting legal obligations in the EU |
The three work well together. Many organizations use the NIST AI RMF to shape their risk approach, ISO 42001 to run and certify the management system, and map both to EU AI Act obligations.
Effort and cost drivers
The effort depends mostly on how many AI systems are in scope, whether you build or only use AI, and whether you already run ISO 27001. Budget for internal time to build the management system, any tooling, and the certification body's audit days, which are set by your scope and headcount. Ask two or three accredited certification bodies for quotes early, as availability for ISO 42001 audits can be limited.
Benefits beyond the certificate
Even before the audit, building an AI management system brings practical gains. You get a complete inventory of the AI your company builds and uses, which often uncovers tools adopted without review. Impact assessments surface risks to customers and users before they become incidents or complaints. Clear ownership speeds up decisions about new AI features. And answering customer AI questionnaires becomes faster because the answers already exist.
When to wait
If AI is experimental with no production use, start with a lightweight AI risk register before full AIMS certification. Build foundation with NIST AI RMF if certification is not yet required.
FAQ
Is ISO 42001 certification mandatory?
No. It is a voluntary standard. Organizations pursue it because customers, partners, investors or regulators expect evidence of responsible AI governance.
Can small companies get ISO 42001 certified?
Yes. The standard scales to the size of the organization and the number of AI systems in scope. Small AI-native companies often certify to win enterprise customers.
Should we get ISO 27001 before ISO 42001?
It is not required, but it helps. ISO 27001 builds the management system foundations, such as document control, internal audit and management review, that ISO 42001 reuses.
How long is an ISO 42001 certificate valid?
Three years, with surveillance audits in the second and third years and a recertification audit before the certificate expires.
What does an ISO 42001 auditor look at first?
In the Stage 1 audit, the certification body reviews your scope, AI policy, AI system inventory, risk and impact assessment method, Statement of Applicability and internal audit plan. Gaps found here should be fixed before the Stage 2 audit.
Does ISO 42001 cover generative AI and AI agents?
Yes. The standard is technology neutral, so it applies to generative models, AI agents and traditional machine learning alike. For generative AI and agents, pay particular attention to intended use, human oversight, monitoring of outputs in production, and transparency to users about when they are interacting with AI.
Can we certify only part of the business?
Yes. You define the scope, for example one product line or a set of AI systems. The scope must be clear and justified, and it should cover the AI that customers and partners care about, otherwise the certificate will not answer their questions.
Disclaimer (legal note)
Informational only, not legal advice. Obligations vary by jurisdiction and use case.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds
