
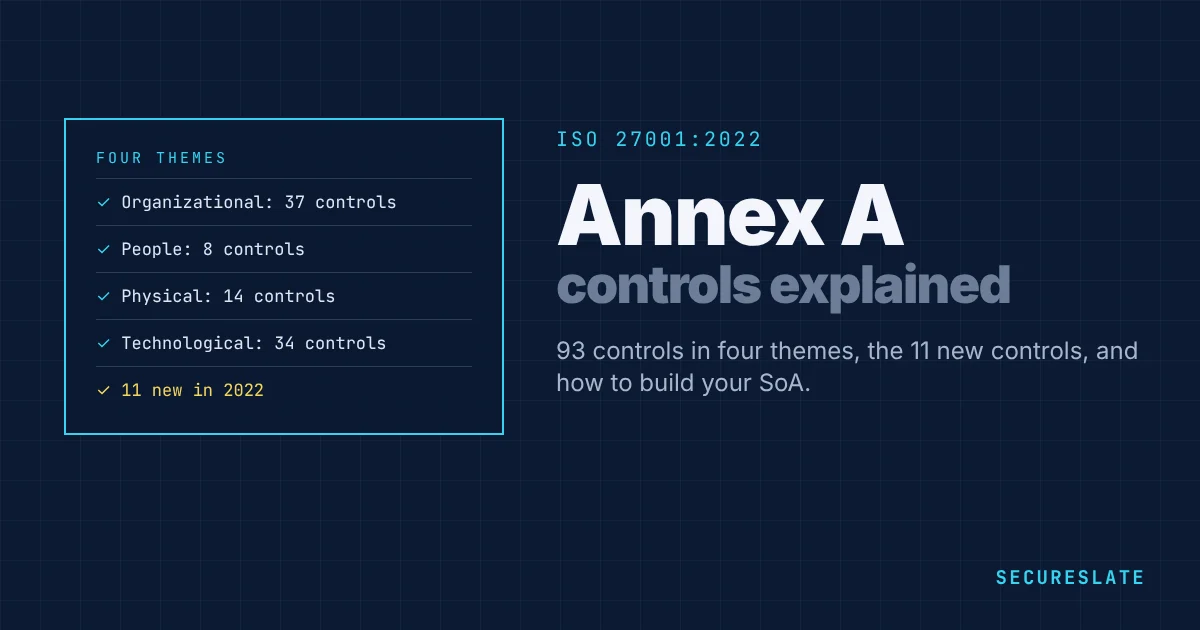
Annex A of ISO/IEC 27001:2022 is the normative control catalog your ISMS uses to treat information security risk. Auditors do not expect you to implement all 93 controls blindly; you select controls based on risk and document your choices in the Statement of Applicability (SoA).
Related guides:
Key takeaways
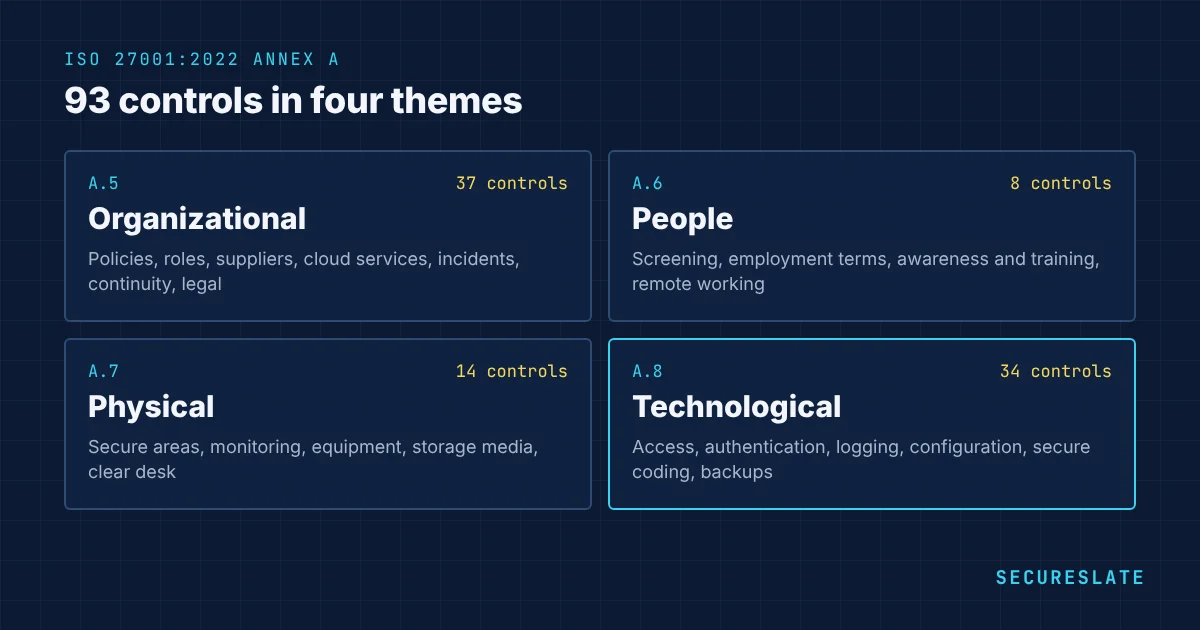
- Annex A contains 93 controls organized into four themes (2022 edition).
- Your SoA lists each control as applicable or not, with justification.
- ISO 27002 provides implementation guidance; ISO 27001 is what you certify against.
- Evidence should show controls are implemented and operating, not only documented.
What is Annex A?
Annex A is the reference set of security controls tied to your risk assessment. Clauses 4–10 describe how you run the ISMS; Annex A describes what safeguards you apply.
The 2013 edition used 114 controls in 14 domains. The 2022 edition consolidated to 93 controls in four themes to align with ISO/IEC 27002:2022.
The four control themes (2022)
| Theme | Focus | Examples |
|---|---|---|
| Organizational (37) | Governance, suppliers, legal, continuity | Policies, supplier security, incident management |
| People (8) | HR security, awareness | Screening, training, remote work rules |
| Physical (14) | Facilities, equipment | Secure areas, equipment handling |
| Technological (34) | Technical safeguards | Access control, logging, secure development, encryption |
Use your risk assessment to decide which controls apply. Document exclusions with clear rationale in the SoA.
Statement of Applicability (SoA)
The SoA is a mandatory artifact that typically includes:
- Control ID and name
- Applicable (yes/no)
- Justification for inclusion or exclusion
- Implementation status
- Reference to policies or procedures
A strong SoA aligns with your risk treatment plan so auditors see a single story from risk → control → evidence.
Evidence auditors expect
For each applicable control, prepare evidence such as:
- Policy approvals and review dates
- Access review exports and MFA configuration
- Ticket samples for change management and incidents
- Training completion reports
- Backup and monitoring screenshots or API-backed tests
Automating evidence collection reduces last-minute audit scrambles. See benefits of compliance automation for ISO 27001.
The 11 new controls in the 2022 edition
The 2022 update merged many older controls and added 11 new ones. Auditors pay close attention to these because many organizations had to build them for the first time.
| Control | Name | What it means in practice |
|---|---|---|
| 5.7 | Threat intelligence | Collect and act on information about threats relevant to you |
| 5.23 | Information security for use of cloud services | Manage security when buying, using and leaving cloud services |
| 5.30 | ICT readiness for business continuity | Plan and test how your technology recovers from disruption |
| 7.4 | Physical security monitoring | Monitor premises for unauthorized physical access |
| 8.9 | Configuration management | Define, apply and monitor secure configurations |
| 8.10 | Information deletion | Delete information when it is no longer needed |
| 8.11 | Data masking | Mask sensitive data where policy or law requires it |
| 8.12 | Data leakage prevention | Detect and prevent unauthorized disclosure of data |
| 8.16 | Monitoring activities | Monitor networks, systems and applications for anomalies |
| 8.23 | Web filtering | Manage access to external websites to reduce exposure to malicious content |
| 8.28 | Secure coding | Apply secure coding principles in software development |
Control attributes
ISO/IEC 27002:2022 tags every control with attributes so you can sort and filter the catalog in ways that suit your organization:
- Control type: preventive, detective or corrective
- Information security properties: confidentiality, integrity and availability
- Cybersecurity concepts: identify, protect, detect, respond and recover
- Operational capabilities: for example asset management, identity and access management or threat and vulnerability management
- Security domains: governance and ecosystem, protection, defence and resilience
Attributes are optional, but they help you spot gaps. For example, a control set with plenty of preventive controls and few detective ones may miss attacks that get through.
How to select controls for your SoA
- Start from your risk assessment. List your top risks and the treatment chosen for each. Controls exist to treat risks, not to fill a checklist.
- Map each treated risk to Annex A. Most risks map to several controls. A phishing risk, for example, links to awareness training (6.3), authentication (8.5) and email and web protections.
- Add controls required by law, contracts or customers. If a customer contract requires encryption at rest, 8.24 applies regardless of your risk scores.
- Mark the rest. For each remaining control, decide whether it applies. A fully remote company with no office may exclude some physical controls, but it must still cover equipment used at home.
- Justify every exclusion. One or two sentences per excluded control, explaining why it does not apply in your scope.
- Record implementation status. Implemented, partially implemented or planned, with a link to the policy or procedure.
The Statement of Applicability template gives you a ready-made layout for all 93 controls.
Annex A for a small SaaS company
For a cloud-based SaaS company of up to 50 people, the controls that usually take the most work are:
- Access control and authentication (5.15 to 5.18, 8.2, 8.5): single sign-on, MFA, role-based access and quarterly access reviews
- Supplier and cloud security (5.19 to 5.23): a vendor inventory, risk-based reviews and cloud provider due diligence
- Logging and monitoring (8.15, 8.16): centralized logs and alerts on suspicious activity
- Secure development (8.25 to 8.29): code review, dependency scanning, secure coding and testing before release
- Configuration and vulnerability management (8.8, 8.9): hardened cloud configurations and patching within defined timelines
- Incident management and continuity (5.24 to 5.30): an incident response plan, postmortems and tested backups
Physical controls are often lighter for remote-first teams, because data centers are covered by the cloud provider's own certifications. You still need to show how you rely on those certifications.
Manage Annex A in SecureSlate
SecureSlate maps Annex A controls to tests, owners, and integrations, so you can maintain your SoA and evidence continuously.
FAQ
Must we implement all 93 controls?
No. Implement controls proportionate to risk and scope, and document the rest as excluded in the SoA.
How does Annex A relate to SOC 2?
Many controls overlap with SOC 2 trust criteria. See mapping common criteria.
What changed between ISO 27001:2013 and 2022 Annex A?
The number of controls fell from 114 in 14 domains to 93 in four themes. Many older controls were merged into fewer, broader ones, and 11 new controls were added, such as threat intelligence, cloud services security and secure coding. No security topic was dropped.
Is the transition to ISO 27001:2022 mandatory?
Yes. Certificates issued against the 2013 version had to transition by October 31, 2025. New certifications use the 2022 version.
What is the difference between Annex A and ISO 27002?
Annex A in ISO 27001 lists the controls and a short statement of each. ISO 27002 explains each control in detail, with its purpose, guidance and attributes. You certify against ISO 27001, and use ISO 27002 as the how-to guide.
How long does it take to implement Annex A controls?
For a cloud-based company of up to 50 people starting from a low base, implementing the applicable controls usually takes three to six months, followed by a period of operation before the certification audit. Companies that already hold SOC 2 can move faster because many controls overlap.
Who should own Annex A controls?
Give each control a named owner where the work happens: engineering for secure development, IT for access and devices, HR for people controls, and leadership for policies and supplier decisions. A compliance lead coordinates the Statement of Applicability and the evidence.
Disclaimer (legal note)
General information only, not audit or legal advice. Control interpretation may vary by certification body and industry.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds
