
GDPR data breach notification requirements force organizations to act quickly when personal data confidentiality, integrity, or availability is compromised. Delays and poor documentation are common enforcement triggers.
Related guides:
Key takeaways
- A personal data breach is any breach leading to accidental or unlawful destruction, loss, alteration, unauthorized disclosure of, or access to personal data.
- Controllers must notify the supervisory authority within 72 hours of becoming aware, when the breach is likely to result in risk to individuals.
- Processors must notify the controller without undue delay after becoming aware.
- You must maintain a breach register even for incidents not reported externally.
This guide covers:
- Definition and examples of reportable breaches
- Authority notification timelines and required details
- Individual notification thresholds
- Operational playbook elements
What counts as a personal data breach?
| Type | Example |
|---|---|
| Confidentiality | Ransomware exfiltrating customer database |
| Integrity | Unauthorized modification of payroll records |
| Availability | Extended outage without backups exposing data loss risk |
Not every security incident is a GDPR breach, but assume breach until assessed. Document discovery time, scope, categories of data, and number of affected individuals.
Notification timelines and content
Processor → controller (Article 33(2))
Processors notify the controller without undue delay after becoming aware, providing details needed for regulatory reporting.
Controller → supervisory authority (Article 33)
| Rule | Detail |
|---|---|
| Deadline | 72 hours after becoming aware (or explain delay) |
| Threshold | Notify if breach is likely to result in a risk to rights and freedoms |
| Phased notice | Initial notification may be incomplete; provide updates as investigation proceeds |
Article 33(3) content typically includes:
- Nature of the breach (categories and approximate numbers)
- DPO or contact point
- Likely consequences
- Measures taken or proposed to address the breach
If notification is not required, document why risk was unlikely.
When to notify affected individuals
Under Article 34, communicate the breach to data subjects without undue delay when it is likely to result in a high risk to them.
| High-risk indicator | Example mitigation in notice |
|---|---|
| Financial fraud risk | Credit monitoring, password reset |
| Sensitive health data exposed | Medical identity theft guidance |
| Credentials leaked | Force password reset, MFA enrollment |
Exceptions to individual notice may apply if you implemented appropriate technical protections (e.g., encryption), subsequent measures eliminated high risk, or notice would involve disproportionate effort (public communication may substitute).
Use clear, plain language, not legalese.
Building a breach response program
- Detection: monitoring, employee reporting, vendor alerts.
- Triage: severity, data categories, legal/comms escalation.
- Containment & recovery: isolate systems, preserve forensics.
- Assessment: risk to individuals; 72-hour clock management.
- Notification: authority, individuals, contracts, insurers.
- Post-incident review: root cause, control improvements, register update.
Run tabletop exercises twice yearly. Align with ISO 27001 incident management where applicable.
The first 72 hours, hour by hour
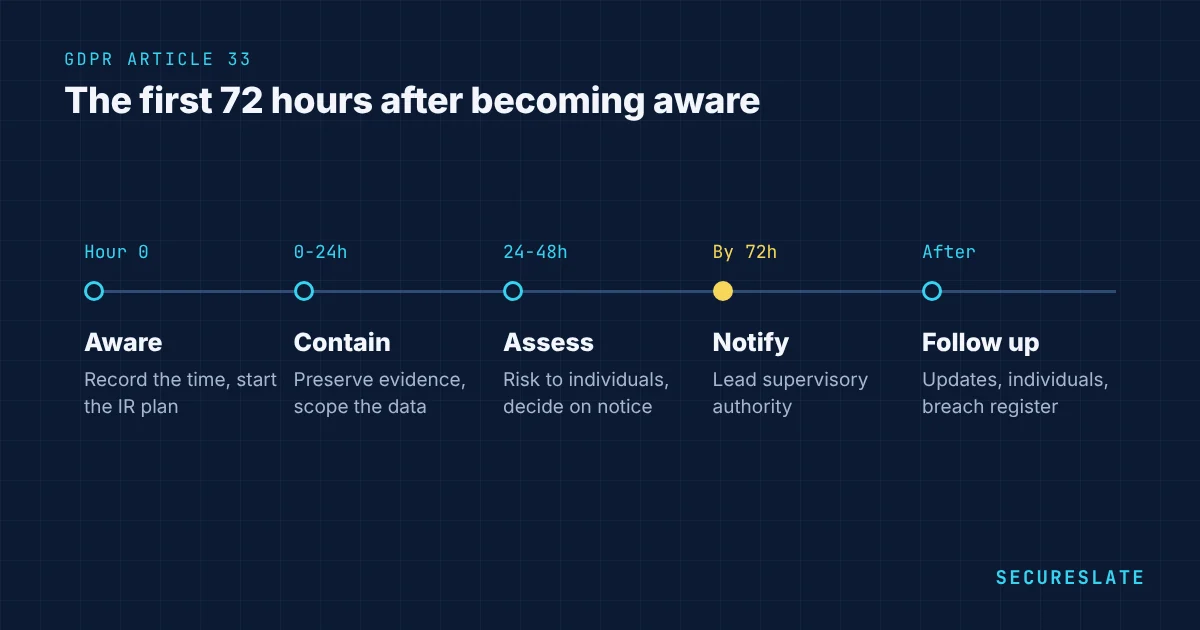
| Time from awareness | Actions |
|---|---|
| Hour 0 | Record the time you became aware. Start the incident response plan and assemble the team, including your DPO or privacy lead |
| Hours 0 to 24 | Contain the breach, preserve evidence, identify the data and people affected as far as possible |
| Hours 24 to 48 | Assess the risk to individuals, decide whether notification to the authority and to individuals is required, draft the notification |
| Hours 48 to 72 | Submit the notification to the lead supervisory authority, even if some details are still unknown, and plan updates |
| After 72 hours | Send further information as the investigation progresses, notify individuals if high risk, record everything in the breach register |
If you miss the 72-hour deadline, the notification must explain the reasons for the delay.
Which authority to notify
Notify the supervisory authority in the EU or EEA country where you have your main establishment. Under the one-stop-shop mechanism, that authority leads for breaches affecting people in several member states. If you have no establishment in the EU, notify the authority in each member state where affected individuals live, and involve your EU representative if you have appointed one. UK GDPR applies the same 72-hour rule, with notification to the Information Commissioner's Office.
Keeping a breach register
Article 33(5) requires you to document every personal data breach, including those you decide not to report. For each breach, record the facts, its effects, the remedial action taken and your reasoning on whether to notify. Supervisory authorities can ask to see this register, and it is often reviewed in ISO 27001 and SOC 2 audits as incident management evidence.
Penalties for getting it wrong
Failing to meet the notification obligations can lead to fines of up to 10 million euros or 2% of worldwide annual turnover, whichever is higher, under Article 83(4). Regulators have fined organizations both for late notification and for failing to document breaches. A rehearsed plan and a clear record of decisions are the best protection.
Processor and contract duties
If you are a processor, your data processing agreements usually set a specific deadline for telling the controller, often 24 to 48 hours, which is stricter than the law. Check each customer contract and make sure your incident response plan follows the shortest deadline.
What to say to affected individuals
Under Article 34, the notice to individuals must be in clear and plain language and include at least: the name and contact details of your DPO or contact point, the likely consequences of the breach, and the measures taken or proposed to deal with it and reduce its effects. Practical advice, such as resetting passwords or watching for phishing, makes the notice more useful. Avoid technical jargon and legal hedging.
Get audit-ready with SecureSlate
SecureSlate helps teams document incident controls, evidence, and remediation tasks alongside broader security and privacy programs.
FAQ
Does the 72-hour clock start at discovery or exploitation?
It starts when the controller is aware with sufficient detail to assess notification. Document when awareness occurred.
Do we notify for encrypted data?
Encryption reduces risk but does not automatically eliminate notification. Assess key compromise and likelihood of re-identification.
Are ransomware attacks always reportable?
Often yes when personal data access or exfiltration is likely. Each incident requires documented risk assessment.
Do we need to notify if only a few people are affected?
The number of people is not the test. Notify the authority if the breach is likely to result in a risk to people's rights and freedoms, even if only one person is affected, for example when sensitive health data is exposed.
Can we notify in stages?
Yes. Article 33(4) allows you to provide information in phases when not everything is known within 72 hours, as long as further details follow without undue delay.
Does a lost unencrypted laptop count as a breach?
Yes, if it contains personal data, because confidentiality may be compromised. Assess the data on it and the likely risk. If the device was encrypted with a strong key that was not compromised, the risk may be low enough that notification is not required, but record the decision in the breach register.
Who decides whether to notify?
The controller does, usually through a small group including the DPO or privacy lead, legal counsel and the incident lead. Record who made the decision and why.
Disclaimer (legal note)
General information only, not legal advice. Breach notification involves jurisdiction-specific supervisory authority procedures and sector rules.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds
