
Short answer: The CCPA HIPAA exemption covers specific information, not whole companies. Protected health information, CMIA medical information, qualifying deidentified patient information and certain clinical research data sit outside the CCPA. Your website analytics, marketing leads, employee records, B2B contacts and non-HIPAA wellness app data can still be fully in scope.
Related guides:
- What is the CCPA, and how will it affect your company?
- CCPA vs CPRA
- HIPAA for HealthTech: a complete guide to compliance
Key takeaways
- The exemption is data-based. Being a HIPAA covered entity or business associate does not take your company out of the CCPA.
- Providers, covered entities and business associates get extra room only for patient information they maintain the same way as PHI or medical information.
- Deidentified patient information is exempt only if it was deidentified under HIPAA's standard and came from patient data, and it loses the exemption if it is reidentified.
- Employee and B2B contact data are no longer exempt; those carve-outs became inoperative on January 1, 2023.
- A field-level data inventory is the only reliable way to draw the line between "HIPAA data" and "CCPA data".
Does the CCPA apply to HIPAA-regulated companies?
Yes, if your company meets the CCPA definition of a business, the CCPA applies to everything that is not specifically exempt.
The CCPA, as amended by the CPRA, applies to a for-profit entity that does business in California and meets at least one threshold in Civil Code Section 1798.140: annual gross revenue above the statutory amount, buying, selling or sharing the personal information of 100,000 or more consumers or households, or earning 50 percent or more of annual revenue from selling or sharing personal information. The revenue figure is adjusted for inflation. As of October 2026, the California Privacy Protection Agency lists it as $26,625,000, effective January 1, 2025.
None of those thresholds mention HIPAA, so a digital health company that holds PHI can still be a CCPA business. The real question is which data sets the CCPA reaches. For the general rules on rights requests and notices, see our CCPA requirements overview.
What exactly does the CCPA exempt?
The CCPA exempts named categories of health information, plus organizations only to the extent they treat patient information like that health information.
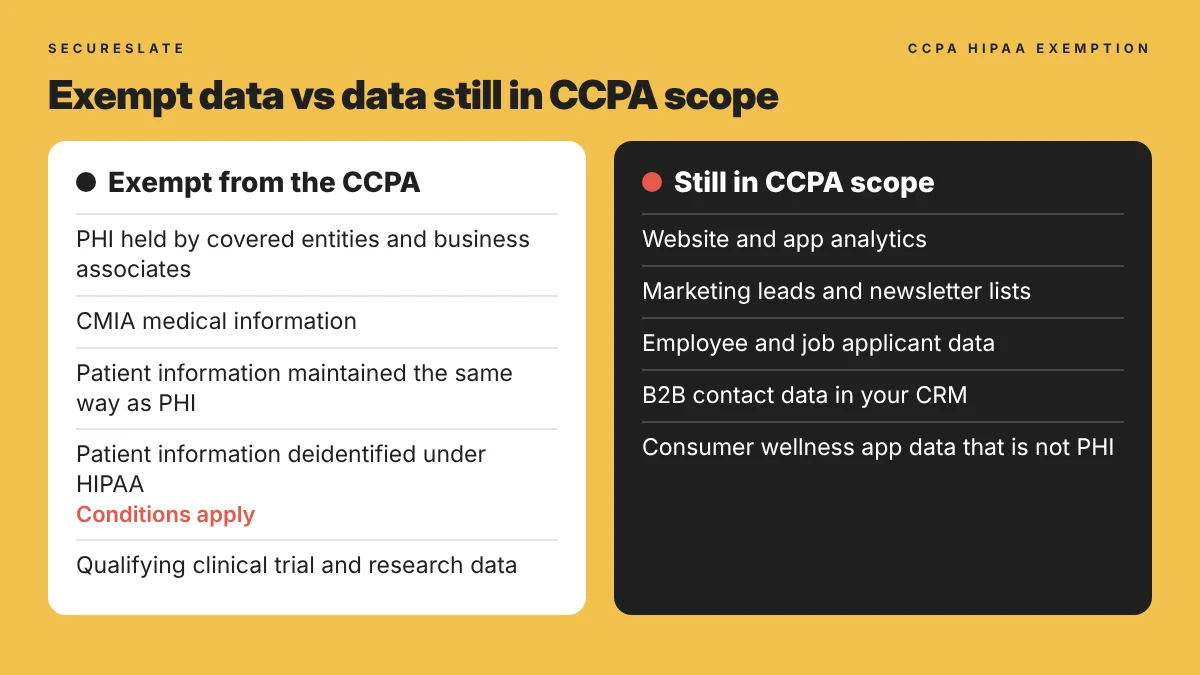
The exemptions sit in Civil Code Sections 1798.145 and 1798.146, with the reidentification rules in Section 1798.148. The terms "covered entity", "business associate" and "protected health information" take their HIPAA meanings from 45 CFR 160.103.
| Data type | Exempt from the CCPA? | Basis |
|---|---|---|
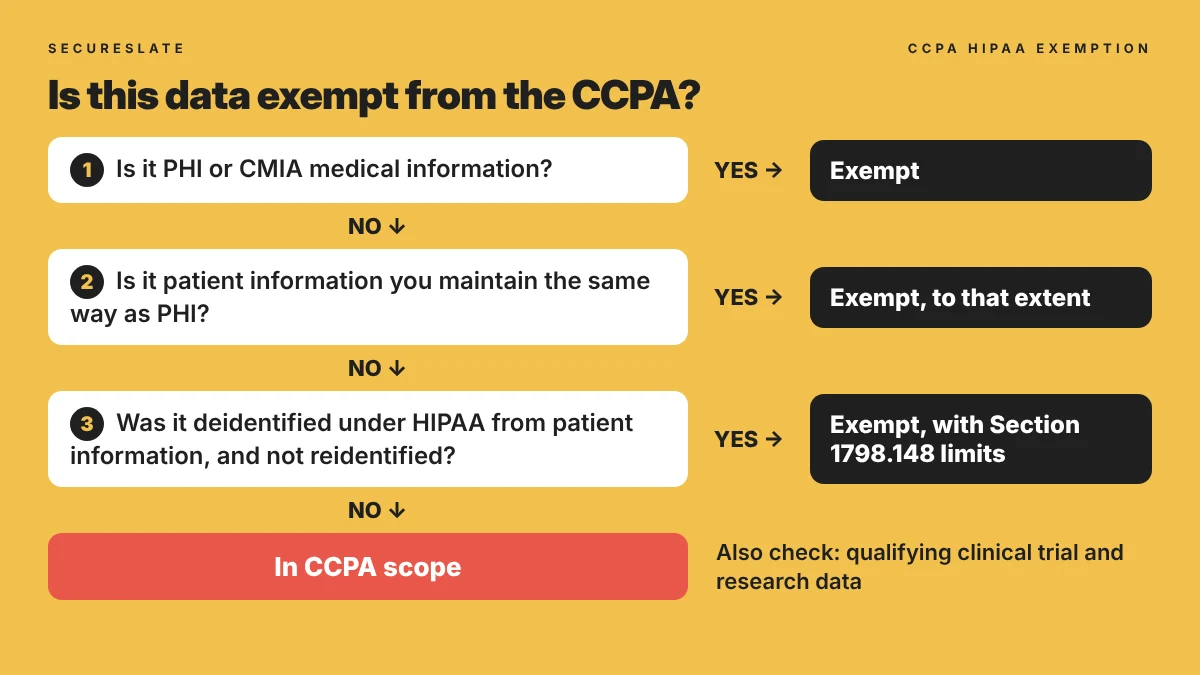
| PHI collected by a HIPAA covered entity or business associate | Yes | Civil Code 1798.145 and 1798.146 |
| Medical information governed by California's Confidentiality of Medical Information Act (CMIA) | Yes | Civil Code 1798.145 and 1798.146 |
| Other patient information a provider or covered entity maintains the same way as PHI or medical information | Yes, to that extent | Civil Code 1798.145 and 1798.146 |
| Patient information a business associate maintains the same way as PHI | Yes, to that extent | Civil Code 1798.146 |
| Patient information deidentified under the HIPAA standard in 45 CFR 164.514 | Yes, if conditions are met | Civil Code 1798.146 and 1798.148 |
| Information collected in qualifying clinical trials or research under the Common Rule, ICH good clinical practice or FDA human subject rules | Yes, if conditions are met | Civil Code 1798.145 and 1798.146 |
| Everything else the business collects | No | General CCPA rules |
The "to that extent" rows matter. Patient data kept in the EHR with HIPAA-grade safeguards rides with the exemption. Patient emails copied into a marketing tool without those protections are no longer maintained in the same manner, which weakens the exemption argument.
Which personal information is not exempt?
Anything that is not PHI, CMIA medical information or one of the other named categories stays in CCPA scope, even inside a HIPAA-regulated company.
Typical HealthTech examples:
- Website and app analytics. Cookie IDs, IP addresses and page events on your public marketing site can be personal information about California consumers. Where tracking touches authenticated patient portals, also check whether the data is PHI, because that changes which law governs it.
- Marketing leads and newsletter lists. Demo requests, webinar sign-ups and gated content downloads are ordinary CCPA data.
- Employee and job applicant data. The CCPA's temporary employee and B2B exemptions in Section 1798.145 became inoperative on January 1, 2023. HR data for California staff and candidates now needs notices and rights handling. HIPAA does not help here either: 45 CFR 160.103 excludes employment records held by a covered entity in its role as employer from PHI.
- B2B contact data. Names, titles and emails of hospital buyers, partners and vendors in your CRM.
- Consumer wellness app data. A direct-to-consumer sleep, fitness or cycle-tracking app that is not acting for a covered entity is usually not a HIPAA business associate, so its user data is not PHI. That data falls under the CCPA, and health data collected and analyzed about a consumer counts as sensitive personal information under Section 1798.140.
Covered entity, business associate or neither: where do you sit?
Your HIPAA role decides how much of your patient-related data can use the exemption, so settle it first.
- Covered entity. Under 45 CFR 160.103, that is a health plan, a health care clearinghouse, or a health care provider that transmits health information electronically in connection with a HIPAA transaction. A covered entity can extend the exemption to patient information it maintains in the same manner as PHI.
- Business associate. A vendor that handles PHI on behalf of a covered entity, such as an EHR add-on, a billing platform or a telehealth backend under a BAA. Section 1798.146 lets a business associate extend the exemption to patient information it maintains the same way as PHI. Its own marketing, HR and sales data remain in scope.
- Neither. A consumer health app selling directly to users, with no covered entity customer behind the data, has no PHI. The CCPA applies in full if the company meets a threshold.
Many HealthTech companies are hybrids, so assess each data flow, not the company as a whole. Our HIPAA for HealthTech guide covers how to decide when you are a business associate.
When is deidentified patient information exempt?
Deidentified patient information is exempt only when it meets HIPAA's deidentification standard and was derived from patient information, and it stays exempt only while nobody reidentifies it.
Section 1798.146 of the CCPA statute sets two conditions. The data must be deidentified in line with 45 CFR 164.514, and it must come from patient information originally collected, created or maintained by an entity regulated by HIPAA, the CMIA or the Common Rule. If the data is later reidentified, it is no longer eligible for the exemption.
Section 1798.148 adds guardrails:
- Reidentifying the data, or trying to, is prohibited except for listed purposes such as treatment, payment or health care operations by a covered entity or business associate, public health, Common Rule research, contracted testing of a deidentification method, or as required by law.
- Reidentified information is subject to the applicable federal and state privacy and security laws.
- A contract to sell or license this deidentified information, where a party is in California, must state that the data includes deidentified patient information, bar the buyer or licensee from reidentifying it, and stop onward disclosure unless the third party accepts the same or stricter terms.
Data that was never PHI cannot use this path. For analytics or AI training sets built from patient data, our HIPAA de-identification guide explains Safe Harbor and Expert Determination.
How do you draw the line with a data inventory?
You draw the line by tagging every data store and flow with the law that governs it, then checking the tag against how the data is actually handled.
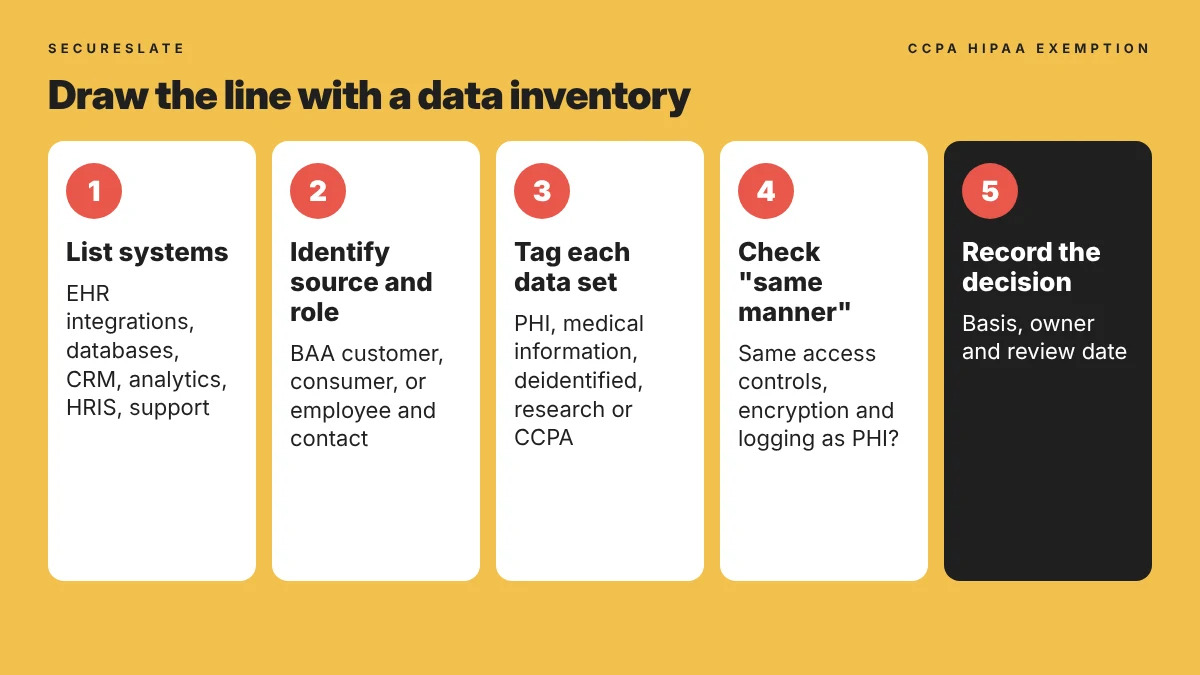
- List systems. EHR integrations, production databases, data warehouse, CRM, marketing automation, analytics tags, HRIS, support desk and log pipelines.
- Identify source and role. For each system, note whether the data came from a covered entity customer under a BAA, directly from consumers, or from employees and business contacts.
- Tag each data set. Use labels such as PHI, CMIA medical information, deidentified patient information, research data, or CCPA personal information. Flag sensitive personal information such as health data from consumer apps.
- Check "same manner". If you rely on the provider or business associate extension, confirm the data gets the same access controls, encryption and logging as your PHI.
- Record the decision. Write down the basis for each exemption claim, an owner and a review date. Repeat when you add a vendor, tag or product line.
Watch for leaks: a support ticket quoting a diagnosis can pull PHI into a system you labelled CCPA-only.
What belongs in your privacy notice and contracts?
Your CCPA privacy policy should describe the personal information you do not treat as exempt, and your contracts should match the role you play for each data set.
- Privacy policy. Section 1798.130 requires an online privacy policy that covers consumer rights and the categories of personal information collected, sold, shared or disclosed. Write it for the in-scope data, and say plainly that PHI is handled under your HIPAA notices or BAAs.
- Notice of privacy practices. Covered entities keep their HIPAA notice for PHI.
- Vendor agreements. For in-scope data, Section 1798.100 requires an agreement with each service provider, contractor or third party that receives personal information. For PHI, keep your BAAs. Some vendors need both.
- Deidentified data deals. Add the Section 1798.148 contract terms to any sale or license of deidentified patient information.
How do HIPAA and CCPA controls overlap?
Most security controls serve both laws, so one control set with two scopes is cheaper than two programs.
| Control area | HIPAA view | CCPA view |
|---|---|---|
| Data inventory and classification | Locate PHI and ePHI | Locate personal and sensitive personal information |
| Access control and reviews | Limit access to PHI | Limit access to in-scope data |
| Vendor management | BAAs and vendor risk review | Service provider and contractor agreements |
| Incident response | Breach notification for PHI | Response for in-scope personal information |
| Retention and deletion | Retention policy for PHI | Deletion requests for in-scope data |
What differs is the consumer-rights workflow. CCPA requests to delete, correct and opt out of sale or sharing (Sections 1798.105, 1798.106 and 1798.120) need an intake process, identity checks and routing that knows which records are exempt. For background on what changed when the CPRA amended the law, read CCPA vs CPRA.
How SecureSlate helps
SecureSlate lets you run HIPAA and CCPA from one control set:
- Multi-framework control mapping with built-in HIPAA. CCPA is set up as a custom framework, so shared controls map to both.
- Agentless read-only cloud integrations and a device agent to collect evidence.
- Access reviews showing who can reach PHI and in-scope personal information.
- Vendor risk management to track which vendors hold PHI under a BAA and which hold CCPA data.
- Risk management, audit management, trust center and security questionnaire automation for hospital buyers.
- Code security and secrets detection to catch leaked credentials.
Start a free SecureSlate trial to map your HIPAA and CCPA controls in one place.
FAQ
Does the CCPA apply to HIPAA covered entities?
Yes, if the covered entity meets the CCPA business definition. The exemption removes PHI, CMIA medical information and patient information maintained the same way, but employee data, marketing data and other personal information remain in scope.
Are business associates exempt from the CCPA?
Only partly. A business associate can treat PHI, and patient information it maintains the same way as PHI, as exempt. Its own website, sales, marketing and HR data are still covered.
Is deidentified patient data exempt from the CCPA?
It is exempt when it was deidentified under HIPAA's standard and derived from patient information. Reidentifying it removes the exemption, and contracts to sell or license it need specific terms under Section 1798.148.
Disclaimer (legal note)
This article is for general information only and is not legal, regulatory or professional advice. Requirements vary by framework, industry and jurisdiction. Consult qualified advisors for your specific obligations.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds
