
Related guides:
- Risk register: what it is and how to keep one
- Inherent vs residual risk
- Free risk assessment template
- Best GRC software solutions (2026)
Key takeaways
- A risk mitigation strategy turns the risks you found into owned actions with deadlines and proof they worked.
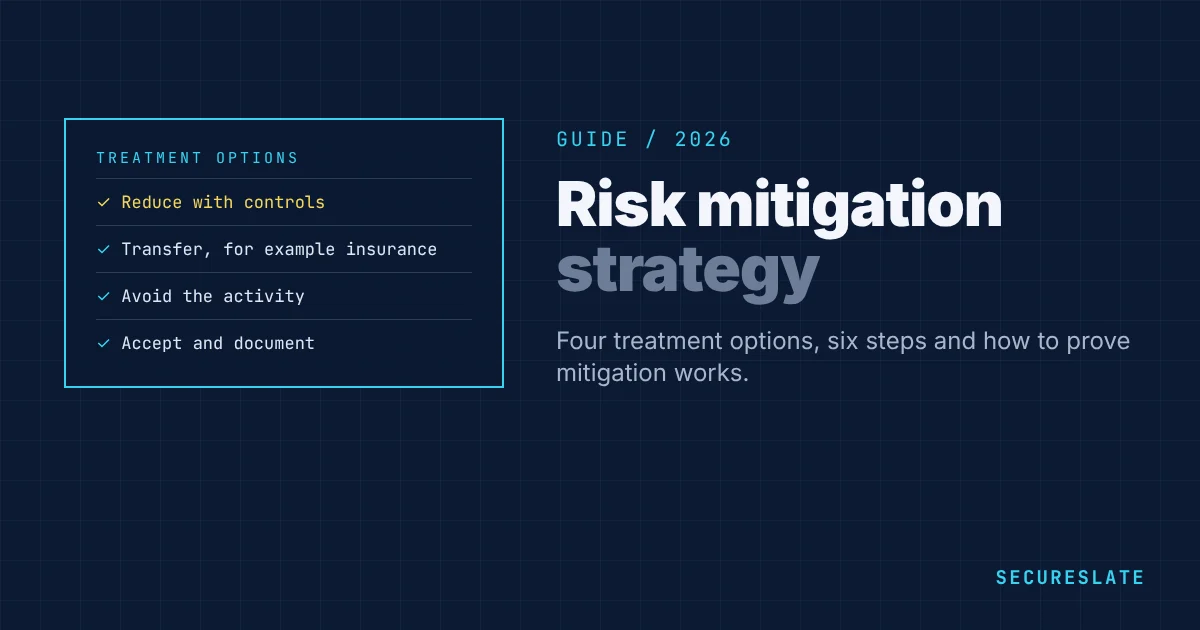
- There are four ways to treat a risk: reduce, transfer, avoid or accept. Mitigation usually means reducing it with controls.
- Prioritize by residual risk and business impact, not by how easy a fix is.
- A mitigation is only finished when you have verified it lowered the risk.
What is a risk mitigation strategy?
After a risk assessment you have a list of risks, each scored for likelihood and impact. A mitigation strategy is the plan for what you will do about each one: which controls to add, who owns them, by when, and how you will know they worked. It is the bridge between knowing your risks and actually lowering them.
The four risk treatment options
| Option | What it means | Security example |
|---|---|---|
| Reduce (mitigate) | Add controls that lower likelihood or impact | Enforce MFA to reduce account takeover |
| Transfer | Shift some of the financial impact to another party | Cyber insurance, or contract terms with a vendor |
| Avoid | Stop the activity that creates the risk | Stop storing card data by using a payment provider |
| Accept | Decide the risk is within your appetite and document it | Accept a low risk on an internal tool, reviewed yearly |
Most strategies combine options. You might reduce ransomware risk with backups and endpoint protection, and transfer part of the remaining financial impact with insurance.
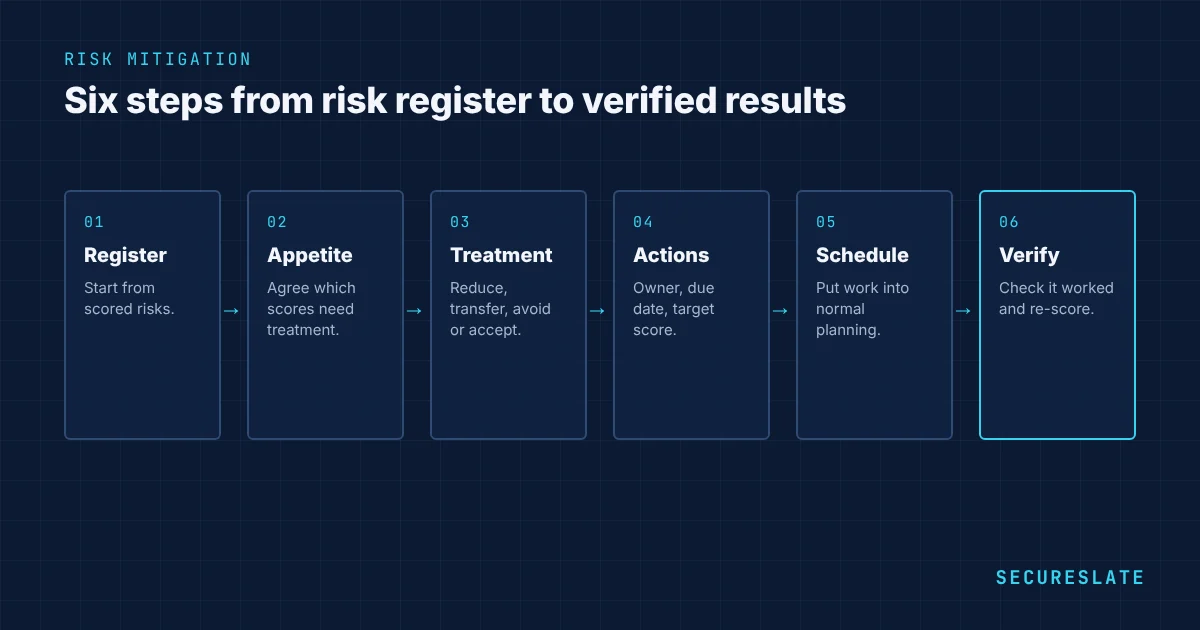
Six steps to build the strategy
- Start from the risk register. Use your scored risks, with inherent risk (before controls) and current residual risk.
- Set your risk appetite. Agree with leadership which scores are acceptable and which must be treated. For example, anything scoring 15 or more on a 25-point scale must be reduced within 90 days.
- Choose a treatment for each risk above appetite, using the four options.
- Define the actions. Write each mitigation as a specific outcome, give it one owner and a due date, and estimate the target residual risk.
- Fund and schedule the work. Put actions into normal team planning and ticketing, not a separate list nobody checks.
- Verify and re-score. Once an action is done, check it works, collect evidence and re-score the risk.
Worked examples
| Risk | Mitigation actions | Owner | Evidence it works |
|---|---|---|---|
| Account takeover through phishing | Phishing-resistant MFA for admins, SSO for all apps, awareness training | IT lead | MFA coverage report at 100%, training completion |
| Data loss from a cloud misconfiguration | Configuration baselines, automated cloud scanning, alerts on public storage | Platform lead | Scan results with no critical findings for 3 months |
| Ransomware stopping operations | Immutable backups, tested restore, endpoint protection on all devices | Engineering manager | Restore test within RTO, device coverage report |
| Former employee keeps access | Offboarding checklist tied to HR system, quarterly access reviews | People ops and IT | Offboarding tickets closed within 24 hours, review sign-off |
| Critical vendor breach | Vendor risk tiers, annual reviews, contract security clauses | Security lead | Reviews completed for all critical vendors |
Prioritizing what to mitigate first
Rank risks by residual score, then adjust for:
- Regulatory and contractual exposure: risks that could break a law or a customer contract move up
- Dependencies: some controls, such as single sign-on, make many other mitigations easier
- Quick wins: low-effort actions that remove a high risk should be done straight away
- Audit timing: risks tied to controls in your next SOC 2 or ISO 27001 audit need to be operating before the audit period
Proving mitigation to auditors
ISO 27001 asks for a risk treatment plan and evidence that it is carried out. SOC 2 expects you to identify risks and show how controls address them. Keep for each risk: the treatment decision, the owner, the action status, the evidence and the updated residual score. Record accepted risks with who approved them, why, and when they will be reviewed.
A risk mitigation plan template
Record each treated risk with these fields, in your risk register or a separate plan:
| Field | Example |
|---|---|
| Risk ID and title | R-07: Account takeover through phishing |
| Inherent score | Likelihood 4 x impact 5 = 20 |
| Treatment | Reduce |
| Actions | Enforce phishing-resistant MFA for admins; SSO for all SaaS apps; quarterly phishing simulation |
| Owner | IT lead |
| Due date | End of Q1 |
| Target residual score | Likelihood 2 x impact 5 = 10 |
| Status | In progress |
| Evidence | MFA coverage report, SSO app list, simulation results |
| Next review | Quarterly |
Keeping the plan in one place, with evidence linked, turns it into audit evidence as well as a working document.
Choosing the right controls
Good mitigations usually combine control types:
- Preventive controls stop the risk happening, such as MFA, least privilege or input validation
- Detective controls spot it quickly when prevention fails, such as alerts, log reviews and integrity checks
- Corrective controls limit damage and restore service, such as backups, incident response and failover
A strategy that relies only on prevention leaves you blind when a control fails. For each high risk, aim for at least one preventive and one detective control. Map each one to your frameworks, for example ISO 27001 Annex A or the SOC 2 criteria, so the same work counts in your audits.
Common mistakes
- Listing mitigations without owners or dates
- Marking actions done without checking they reduced the risk
- Accepting risks informally, with no record of who decided
- Treating the plan as a one-off exercise instead of reviewing it at least quarterly
How SecureSlate helps
SecureSlate links each risk to its treatment, owner, controls and evidence, tracks action status and reminds owners when reviews are due. Residual scores update as controls pass, so you can show auditors and leadership that risks are actually going down.
FAQ
What is the difference between risk mitigation and risk management?
Risk management is the whole process: identifying, assessing, treating and monitoring risks. Risk mitigation is one part of it, reducing a risk through controls or other actions.
How often should a risk mitigation plan be reviewed?
Review progress at least quarterly, and update the plan after major changes, incidents or a new risk assessment.
Can a risk be fully eliminated?
Rarely. Controls usually reduce a risk to an acceptable level. Only avoiding the activity removes the risk completely.
Who should approve accepted risks?
Someone with the authority to own the consequence, usually a member of the leadership team, and the decision should be recorded with a review date.
How do I measure whether mitigation worked?
Re-score the risk once controls are in place, using evidence such as coverage reports, test results or a drop in related incidents. If the residual score has not fallen to the target, the mitigation is not finished.
What is a risk appetite statement?
A short statement, approved by leadership, of how much risk the company is willing to accept in pursuit of its goals, often expressed as score thresholds that trigger treatment.
Disclaimer (legal note)
General information only, not legal, audit, or attestation advice. Requirements depend on your contracts, system boundary, and assessor guidance.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds
