
A SOC 2 compliance questionnaire is a list of questions about your security controls, grouped by the AICPA Trust Services Criteria. Companies use it in two ways: to check their own readiness before a SOC 2 audit, and to assess whether a vendor meets SOC 2 expectations. This guide gives you 60+ questions organized by criteria, explains how to answer them well, and shows how to automate SOC 2 questionnaires so they stop eating your team's time.
Related guides: SOC 2 self-assessment checklist · Vendor security questionnaire template · How to automate security questionnaires · SOC 2 controls list
Key takeaways
- Organize SOC 2 questions by the Trust Services Criteria: Security (Common Criteria), Availability, Confidentiality, Processing Integrity and Privacy.
- Use it internally to find gaps before an audit, and externally to review vendors that handle your data.
- Good answers are specific, true and linked to evidence.
- Keep an answer library and automate repeat questionnaires instead of writing answers from scratch.
Two uses of a SOC 2 questionnaire
| Use | Who fills it in | Goal |
|---|---|---|
| Readiness questionnaire | Your own team | Find control gaps before the auditor does |
| Vendor questionnaire | Your vendors | Check that suppliers handling your data meet SOC 2 expectations |
If a vendor already has a SOC 2 Type 2 report, review the report first and send only questions it does not answer. See how to review a vendor SOC report.
SOC 2 questionnaire: Security (Common Criteria)
Control environment and governance (CC1, CC2)
- Is there a named owner for information security, with leadership oversight?
- Are security policies approved, published and reviewed at least yearly?
- Do employees and contractors acknowledge policies at hire and yearly?
- Are background checks performed where lawful?
- Is security awareness training completed at onboarding and yearly?
- How are security responsibilities communicated to customers?
Risk assessment (CC3)
7. Is there a documented risk assessment, updated at least yearly?
8. Are fraud risks considered?
9. Are risks from significant changes, such as new products or vendors, assessed?
10. Are risk treatment decisions approved and tracked?
Monitoring (CC4)
11. How are controls monitored between audits?
12. Are control failures tracked to resolution?
13. Is an internal review or audit performed?
Control activities and access (CC5, CC6)
14. Is single sign-on used for company systems?
15. Is MFA enforced for all users, and phishing-resistant MFA for admins?
16. Are access requests approved before access is granted?
17. Is access removed within a set time when someone leaves?
18. Are user access reviews performed at least quarterly for in-scope systems?
19. Is privileged access limited and logged?
20. Is customer data encrypted at rest and in transit?
21. Are encryption keys managed and rotated?
22. Are laptops encrypted and managed?
23. Is physical access to offices or data centers controlled, or inherited from a cloud provider?
System operations (CC7)
24. Are security events logged centrally and retained?
25. Are alerts reviewed and escalated?
26. Are vulnerability scans run regularly, with fix timelines by severity?
27. Is a penetration test performed at least yearly?
28. Is there an incident response plan, tested at least yearly?
29. Are customers notified of incidents within a defined time?
Change management (CC8)
30. Are code changes peer reviewed before production?
31. Are changes tested and approved?
32. Are emergency changes documented and reviewed afterward?
33. Are production and development environments separated?
Risk mitigation and vendors (CC9)
34. Are critical vendors identified and reviewed before onboarding and yearly?
35. Are vendor SOC 2 reports reviewed, including complementary user entity controls?
36. Is there business continuity and disaster recovery planning?
37. Is cyber insurance in place?
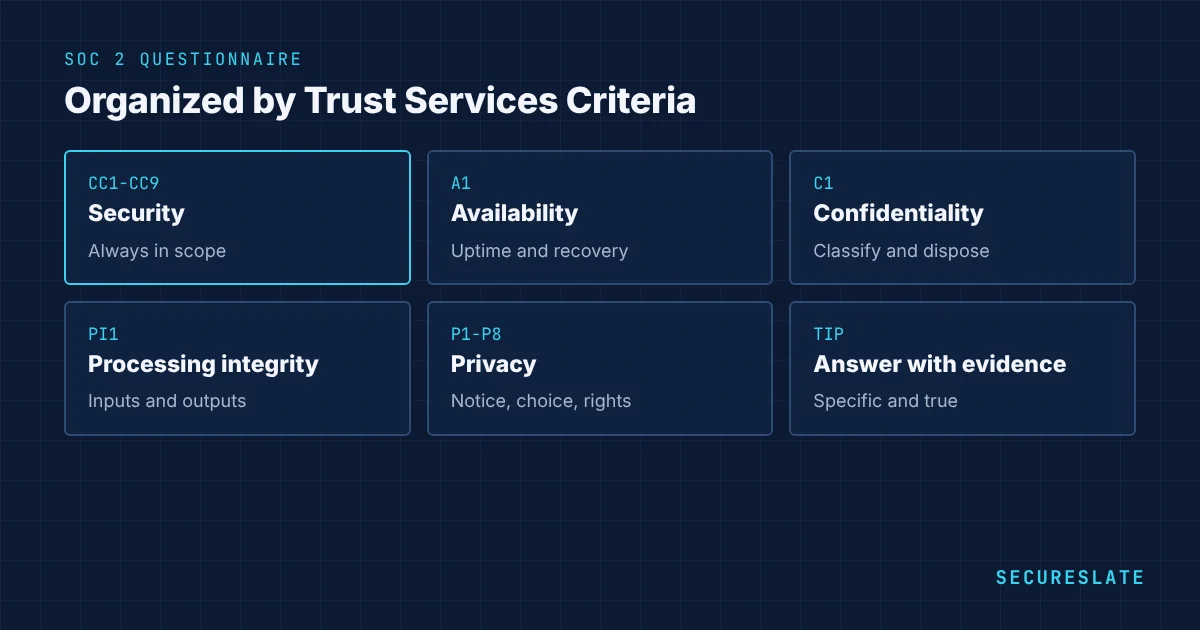
Availability questions
- What uptime commitment is given to customers?
- Is capacity monitored with alerts?
- Are backups automated, encrypted and tested by restoring?
- What are the recovery time and recovery point objectives?
- Is the disaster recovery plan tested?
Confidentiality questions
- Is confidential information identified and classified?
- Is access to confidential information restricted by role?
- Is confidential data deleted securely when no longer needed?
- Are confidentiality obligations included in contracts with staff and vendors?
Processing integrity questions
- Are data inputs validated for completeness and accuracy?
- Are processing errors detected and corrected?
- Are outputs reviewed for accuracy where it matters to customers?
Privacy questions
- Is there a privacy notice describing collection and use of personal information?
- Is consent obtained where required?
- Can individuals access, correct and delete their data?
- Is personal data retained only as long as needed?
- Are sub-processors disclosed?
- Are privacy incidents handled and notified?
How to answer a SOC 2 questionnaire well
- Be specific. "MFA is enforced for all users through our identity provider; admins use hardware keys" beats "Yes."
- Point to evidence. Mention the control, policy or report section that proves the answer.
- Be honest about gaps. Say what is planned and by when, and describe compensating controls.
- Keep answers consistent with your SOC 2 report, policies and trust center. Reviewers compare them.
- Mark not applicable answers with a reason, such as physical security inherited from your cloud provider.
Example answers
| Question | Strong answer |
|---|---|
| Is customer data encrypted at rest? | Yes. Customer data is encrypted with AES-256 using our cloud provider's key management service. Keys rotate yearly. |
| How quickly is access removed when someone leaves? | Access is removed on the last working day through our identity provider, triggered by the HR system. Quarterly reviews confirm no leftover accounts. |
| Do you perform penetration tests? | Yes. An independent firm tests the application and infrastructure yearly. A summary letter is available in our trust center under NDA. |
| How are customers notified of incidents? | Affected customers are notified without undue delay and within 72 hours of confirming a breach of their data, as set out in our DPA. |
SOC 2 readiness score from the questionnaire
Score each question as in place, partly in place or not in place. Anything not in place in the Security section needs fixing before a Type 1 audit. Items partly in place need consistent operation over the period before a Type 2. Many teams turn the result into a project plan with owners and dates.
Automating SOC 2 questionnaires
Customers send SOC 2 questionnaires in many formats: spreadsheets, portals and standard forms such as the SIG and CAIQ. An answer library tied to your controls lets software draft answers in minutes. Review each draft, update the library when controls change, and share your trust center link first so many reviewers never send a questionnaire at all.
How SecureSlate helps
SecureSlate turns this questionnaire into tracked SOC 2 controls with automated evidence, and its questionnaire automation drafts answers to customer SOC 2 questionnaires from your real controls, shared alongside a trust center.
FAQ
What is a SOC 2 questionnaire?
A set of questions about security, availability, confidentiality, processing integrity and privacy controls, used to check readiness for a SOC 2 audit or to assess a vendor.
Does a SOC 2 questionnaire replace a SOC 2 report?
No. A questionnaire is self-reported. A SOC 2 report is an independent auditor's opinion. Buyers prefer the report and use questionnaires to cover gaps.
Which SOC 2 criteria should a questionnaire cover?
Always Security (the Common Criteria). Add Availability, Confidentiality, Processing Integrity and Privacy if they are in scope for the audit or relevant to the vendor.
How can SOC 2 questionnaires be automated?
Keep an answer library tied to your controls and evidence, and use software to draft answers to new questionnaires from it. Review the drafts before sending.
What is a SOC 2 compliant survey tool?
A survey or form tool whose vendor holds a SOC 2 report covering it, so you can collect data from customers or employees while meeting your own vendor management requirements.
How long should it take to answer a SOC 2 questionnaire?
With an answer library and automation, many questionnaires take hours. Without one, a 200-question spreadsheet can take a week of back and forth.
Can we send this questionnaire to our vendors?
Yes. Trim it to the criteria relevant to what each vendor does, and accept their SOC 2 Type 2 report in place of questions it already answers.
Is there an official SOC 2 questionnaire?
No. The AICPA publishes the Trust Services Criteria, not a questionnaire. Companies build their own or use standard forms such as the SIG or CAIQ.
Disclaimer (legal note)
This article is for general information only and is not legal, regulatory, or professional advice. Requirements vary by framework, industry, and jurisdiction. Consult qualified advisors for your specific obligations.
Need compliance without the complexity?
SecureSlate automates ISO 27001, SOC 2, GDPR, HIPAA, and more. Built for growing teams. See it in action.
Find compliance gaps in 30 seconds